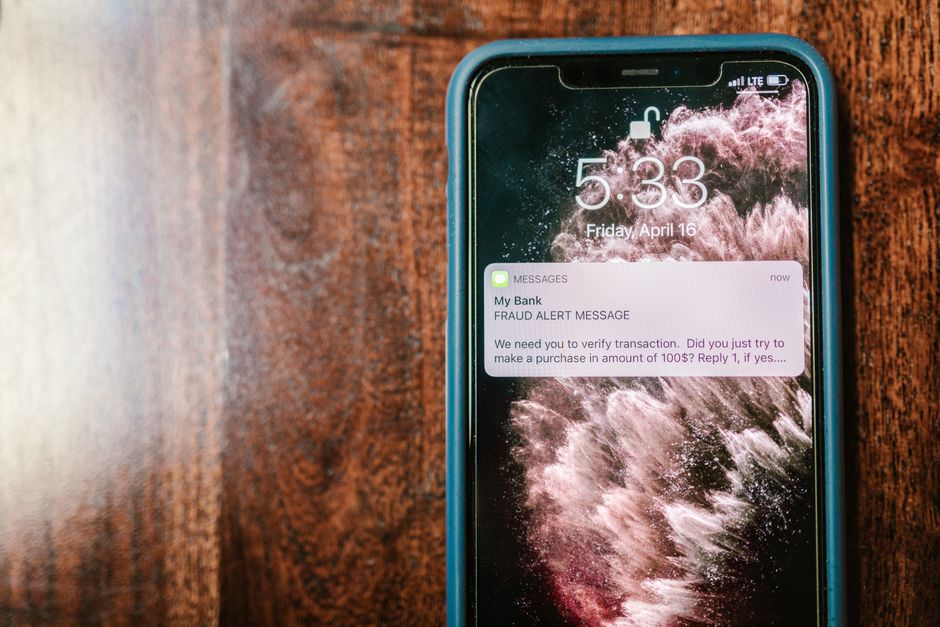
Two-Factor Authentication for Online Banking and Shopping
Two-factor authentication (2FA) is a security process in which users provide two different authentication factors to verify themselves. In the context of online banking and shopping, 2FA adds a critical layer of protection beyond just a password. This method is designed to reduce the likelihood of unauthorized access to sensitive financial information, even if a password is compromised. By requiring a second form of verification, such as a code from a mobile app or a hardware token, institutions aim to ensure that the person accessing the account is indeed the legitimate user.
The importance of 2FA has grown as cyber threats become more sophisticated. Passwords alone are increasingly vulnerable to phishing, brute force attacks, and data breaches. When a password is stolen, it can be used to access multiple accounts if the same password is reused. Two-factor authentication mitigates this risk by requiring something the user has (like a smartphone or a hardware token) in addition to something they know (the password). This article explores the setup and use of app-based and hardware token verification methods for online banking and shopping, emphasizing best practices and considerations for implementation.
In the United States, financial institutions and retailers are increasingly adopting 2FA to comply with regulations and to protect customer data. However, user adoption and proper configuration are essential for effectiveness. This guide provides an overview of the available options, steps for setup, and factors to consider when choosing between app-based and hardware token methods. The focus is on practical, actionable information that can help individuals and organizations enhance their security posture.
Understanding Two-Factor Authentication
Two-factor authentication combines two of three possible authentication factors: something you know (password), something you have (a device), and something you are (biometrics). For online banking and shopping, the most common implementation uses a password as the first factor and a code generated by an app or hardware token as the second. This combination significantly increases the difficulty for unauthorized users to gain access, as they would need both the password and the physical device to complete the login process.
App-based 2FA typically involves installing an authenticator app on a smartphone. The app generates time-based one-time passwords (TOTP) that are valid for a short period, usually 30 seconds. Hardware tokens are physical devices that generate codes, often similar to a key fob, and may use one-time passwords or push notifications. Both methods have strengths and weaknesses, and the choice between them depends on the user’s technical comfort, the value of the accounts being protected, and the support provided by the service provider.
It is important to note that 2FA is not foolproof. Attackers may use techniques like phishing to intercept codes or SIM swapping to hijack SMS-based 2FA. Therefore, app-based and hardware token methods are generally considered more secure than SMS-based 2FA, as they are less susceptible to interception. However, proper implementation and user education are critical to realizing the full benefits of any 2FA method.
Setting Up App-Based Verification
App-based verification is a popular and convenient form of 2FA. To set it up, users typically need a smartphone and an authenticator app such as Google Authenticator, Authy, or Microsoft Authenticator. The process generally begins in the security settings of the online banking or shopping account, where the user enables two-factor authentication and selects the app-based option. The service then displays a QR code, which the user scans with the authenticator app. This establishes a shared secret between the app and the service.
Once set up, the app will generate a new code every 30 seconds. When logging in, the user enters their password and then the current code from the app. Some services offer push notifications as an alternative, where the user simply approves a login request on their phone. This method reduces the need to manually enter codes and can streamline the user experience while maintaining security.
When configuring app-based verification, users should consider the following best practices:
- Use a reputable authenticator app from a trusted vendor. Ensure the app is downloaded from the official app store and has good reviews.
- Enable backup options, such as exporting the app’s data or linking it to a cloud account, to avoid losing access if the phone is lost or replaced.
- Secure the smartphone with a PIN, password, or biometric lock to prevent unauthorized access to the authenticator app.
- Regularly update the app and the phone’s operating system to patch security vulnerabilities.
- Be cautious of phishing attempts that ask for codes; legitimate services will not ask for codes via unsolicited messages or calls.
App-based verification offers a good balance between security and usability. It is generally free, easy to set up, and does not require additional hardware. However, it relies on the smartphone being charged and available, which may be a consideration for some users. Additionally, if the phone is compromised by malware, the codes could be intercepted, although this is less common than SMS interception.
Implementing Hardware Token Verification
Hardware tokens are physical devices that generate authentication codes. They are often used in corporate environments but are also available for consumer banking and shopping accounts. A hardware token may be a USB device, a key fob, or a smart card reader. These devices are designed to be tamper-resistant and may require a PIN to activate, adding another layer of security. Hardware tokens are particularly useful for high-value accounts or for users who prefer not to rely on a smartphone for authentication.
To set up a hardware token, users typically need to obtain the device from their bank or service provider. The setup process involves registering the token with the account, which often requires entering a serial number or scanning a QR code. Once registered, the token will generate codes that are entered during login. Some tokens use a challenge-response mechanism, where the user enters a challenge provided by the service, and the token generates a response.
When using hardware tokens, consider the following:
- Keep the token in a secure location, similar to how you would protect a credit card or key.
- Be aware that losing the token may require a replacement process, which could involve contacting customer support and verifying identity.
- Check if the token has a battery and monitor its lifespan; some tokens have non-replaceable batteries that last several years.
- Follow the provider’s instructions for proper use and care to avoid damage.
- If the token requires a PIN, choose a strong PIN and do not share it with anyone.
Hardware tokens provide strong security because they are separate from the user’s computer or phone, reducing the risk of malware interception. However, they come with added cost and logistical considerations, such as distribution and replacement. For users who manage multiple accounts, carrying multiple tokens may be inconvenient. Some organizations are moving toward standards like FIDO2, which allows hardware security keys to be used across multiple services, but adoption in banking and shopping is still evolving.
Best Practices for Secure Authentication
Whether using app-based or hardware token verification, certain best practices can enhance the overall security of online banking and shopping. First, users should ensure that their primary password is strong and unique, not reused across different sites. A password manager can help generate and store complex passwords. Second, users should enable 2FA on all accounts that offer it, prioritizing financial and email accounts, as email is often used for password resets.
Third, users should be vigilant about phishing attacks. Even with 2FA, attackers may attempt to trick users into revealing their codes or approving fraudulent transactions. Always verify the legitimacy of requests by contacting the institution directly through official channels. Fourth, users should regularly review account activity and enable alerts for logins or transactions. Prompt notification of unusual activity can allow for quick response.
Additionally, users should consider the recovery options for their 2FA method. For app-based 2FA, backup codes or cloud backups are essential. For hardware tokens, knowing the replacement process and having a backup method (such as a secondary token or a trusted contact) is prudent. It is also advisable to keep recovery information up to date, such as phone numbers and email addresses.
For organizations, implementing 2FA for customer accounts requires careful planning. Providing clear instructions, offering multiple 2FA options, and supporting users through the setup process can improve adoption. Regular security awareness training and communication about the importance of 2FA can also help. SecurePath offers resources and guidance on implementing robust authentication measures, though specific outcomes depend on individual implementation and usage.
Choosing the Right Method for Your Needs
Selecting between app-based and hardware token verification depends on various factors, including the value of the accounts, the user’s technical proficiency, and the level of risk tolerance. App-based verification is generally more accessible and cost-effective, making it suitable for a wide range of users. It leverages existing smartphones and provides a good level of security when best practices are followed. However, it may not be ideal for users who are uncomfortable with smartphone apps or who have concerns about phone-based threats.
Hardware tokens offer a higher level of assurance for high-risk accounts, as they are physically separate and less susceptible to remote attacks. They are often recommended for individuals who manage large sums or for businesses that require stringent security controls. However, the cost and logistics of distributing and managing tokens can be a barrier. Some institutions offer hardware tokens as an option for customers who request them, while others may require them for certain transactions.
In some cases, a combination of methods may be appropriate, such as using app-based 2FA for everyday banking and a hardware token for high-value transactions. Users should check with their bank or shopping platform to see what options are available. It is also important to consider the fallback mechanisms in case the primary method fails; for example, having backup codes or a secondary device can prevent lockouts.
Ultimately, the effectiveness of any 2FA method depends on proper setup, user vigilance, and the security practices of the service provider. No single method is perfect, but adding a second factor significantly raises the bar for attackers. By understanding the strengths and limitations of each approach, users can make informed decisions that align with their security needs and lifestyle.